Jason Hiner
Jason Hiner is the Editor-in-Chief and Chief Content Officer of The Deep View. He's an award-winning journalist who has spent his career analyzing how tech has reshaped society. He covered AI for over a decade at ZDNET and CNET as it evolved from research labs to enterprise infrastructure to a daily reality for over a billion people. He came to The Deep View to cover AI every day and build a next-generation media company.
Articles
Nvidia's secret weapon for accelerating AI factories
Nvidia has figured out a way to build AI factories a lot faster.
These massive data centers bring together billions of dollars of computing equipment into a facility where a ton of different tech, power, cooling, and logistical systems have to work together seamlessly. Managing that kind of complexity is one of Nvidia's strengths.
With chip design, Nvidia architects everything virtually in a simulated environment long before the first manufacturing process starts. And since today's chips and processors have become enormously complex, that orchestration is where the magic happens, in terms of speed, efficiency, and innovation.
Nvidia is applying this same mindset to building AI factories by partnering with Siemens and implementing digital twins, or virtual replicas of real-world environments. This allows Nvidia and its partners, such as hyperscalers and neoscalers, to simulate these elaborate facilities ahead of time and rehearse all of the processes that make them work.
"You’re really building a data center scale computer, along with all the technology, it’s not just about the GPU," Vladimir Troy, Nvidia's VP of AI infrastructure, told The Deep View. "This is the fundamental part that I think people miss about accelerated computing. If you just optimize the GPU, then you have the fastest GPU, and your bottlenecks could be everywhere else."
Digital twins are the key to making it all happen by allowing engineers to simulate a facility's physical behavior. Siemens brings the simulation, automation, and industrial engineering expertise while Nvidia brings the accelerated computing, its Omniverse platform, and the experience with synthetic data.
"You can improve the time-to-token by [roughly] 40% if you’re using digital twins," Ales Alajbegovic, global program manager of industrial metaverse for Siemens, told The Deep View. "If you don’t use digital twins, I don’t even know how you can build this."
In this case, time-to-token is referring to the period from the time you break ground on the facility to the time it's serving its first useful AI query for the public. That metric is critical because AI usage continues to scale up, despite public sentiment turning negative on AI. In the past 18 months, we've gone from roughly 15% of the global population regularly using AI to 19%. And in places like Singapore and UAE, two-thirds of the population are already using it regularly.
All of that usage is putting tremendous strain on today's data centers. Without more data center capacity, the industry faces the risk of AI queries taking much longer to run, the most powerful models being limited to those who can afford to pay a premium, and slowing down some of the most promising uses of AI for science and healthcare. That's why so many of the world's leading cloud and data center companies are building out future capacity, despite limitations on power and component shortages for RAM and data storage.
"The demand is huge," said Alajbegovic. "Right now the whole industry … is running to build them."
Nvidia estimated that there are well over 100 projects underway globally.
Our Deeper View
Of course, the only thing less popular than AI among the general public right now might be data centers. However, as Nat Rubio-Licht has written, the backlash against data centers might also just be the public's easiest way to register its larger concerns about AI. It doesn't help that there are false narratives proliferating about AI using up community water supplies, for example. But the leaders of the AI industry also need to do a much better job of explaining how AI will benefit humanity, without resorting to unbelievable hyperboles about AI curing all diseases or leading to unlimited abundance and prosperity. People just aren't buying that. The work that Nvidia and Siemens are doing to build data centers faster is also making them enormously more efficient. However, with only so much power, water, and construction capacity, those efficiency gains are out of pure necessity. Still, it's also a great story about building responsibly and not wasting resources, while also making sure there's enough compute to power the AI of the future and keep it broadly accessible and affordable.
How open models change the economics of AI
Companies want to own the intelligence that makes their business valuable. So what will that mean for the AI models they use, and the systems they build around them?
In this episode of The Deep View Conversations, we sit down with Justin Boitano, VP of enterprise AI at Nvidia, to explore why NVIDIA is investing in open models and how enterprises are turning them into specialized intelligence.
Boitano talks about why NVIDIA makes Nemotron's datasets, training techniques and model weights openly available, how proprietary business knowledge can become a competitive advantage, and why lower token costs can unlock much greater demand for AI.
The conversation also examines why the agent harness that manages tools, memory and execution can matter as much as the model itself. Boitano shares how Nvidia worked with CrowdStrike on AI models for cybersecurity, why AI incidents need the equivalent of an aviation flight recorder, and how OpenShell moves agent controls into the infrastructure layer.
Other topics covered:
• Why NVIDIA is building open models alongside its chip business
• What Nemotron needs to compete with China's open models
• Owning institutional knowledge, protecting data and controlling AI costs
• How model development helps NVIDIA improve hardware efficiency
• Why harness engineering is becoming a new frontier for AI
• Moving cybersecurity from finding bugs to verifying and fixing them
• Transparency and learning from AI incidents
• OpenShell, sandboxing and enforceable limits on agent access
• How Justin uses Hermes as an AI chief of staff
• Jensen Huang's approach to priorities and team alignment
If you're deciding how to build enterprise AI, where your company's competitive advantage comes from, or how to give agents useful access without giving them unlimited control, this conversation offers a perspective from Nvidia's work across the ecosystem.
📺 Watch on YouTube
🎧 Listen in your favorite podcast player
Subscribe to Deep View Conversations for interviews with the leaders shaping the future of AI, business, and technology: https://tdv.transistor.fm/
Why Anthropic's open hardware move exploded in interest
Anthropic is the only one of three major frontier AI labs in the US that doesn't offer an open model. But a recent Anthropic move shows that the company does still want to support open ecosystems.
In a move that has largely flown under the radar, Anthropic announced its Model Hardware Standard (MHS) at the end of August as "the MCP for hardware," as Alek Kemeny, a member of technical staff on Anthropic's Beneficial Deployments team, told The Deep View.
MCP (Model Context Protocol) is an open standard that enables AI models and agents to connect to external tools, data, and services through a common interface that Anthropic developed and open-sourced in November 2024. It has since become an industry standard with around 500 million monthly SDK downloads, and has only become more relevant in recent months with the rise of AI agents that are hungry for context and data.
MHS hopes to do for hardware and devices what MCP has done for software and services. It wants to give AI models and agents a common interface for interacting with thousands of otherwise incompatible systems. While MHS was conceived as a way for scientists to drive lab automation using Claude, the response to the announcement has been intense, the Anthropic team said, and has spread far beyond science labs. Kemeny noted that in the first two weeks after the announcement, Anthropic received 30x the number of organizations requesting to participate than Anthropic had originally planned for.
And the types of organizations that applied spanned a lot of different industries from semiconductors, advanced manufacturing, automotive, food processing, aerospace, energy, and critical infrastructure.
Some of the benefits already being reported include:
- Stabilizing quantum computers: QuEra used MHS to help Claude develop a program for controlling lasers used in its quantum computers. The finished program restored the laser correctly in 695 of 700 tests. Difficult recoveries took 10 to 14 seconds, compared with 5 to 10 minutes for a human expert.
- Running lab experiments automatically: Carnegie Mellon researchers used MHS to connect a liquid handler, plate reader, robotic arm, and cameras. An AI agent ran an experiment, decided the first result was not good enough, changed the concentration range and tried again on its own. The test used colored dye as a stand-in for a drug candidate. CMU says testing real drug candidates is the next step.
- Giving labs a 24/7 operator: A University of Washington PhD student connected six lab instruments through MHS in less than a week. He built a system where AI can watch a DNA amplification experiment and stop it at the right time. He also connected a robotic arm and liquid handler so they could move lab plates safely between machines.
"Beneficial Deployments is really charged with seeing, owning, and championing our public benefit mission, and ensuring that the benefits of AI extend to positive outcomes for humanity," Jonah Cool, head of our partnerships and deployment at Anthropic, told The Deep View during the same interview with Kemeny. "As it pertains to science, a lot of our work is really inspired by the guiding light of the essay that our CEO Dario [Amodei] wrote, Machines of Loving Grace."
Our Deeper View
Anthropic has gained a reputation for being anti-open-source, mostly due to the fact that Amodei has raised safety concerns about open-weights models. However, the successful open-source rollout of MCP provides a counterweight, as does Anthropic's commitment to and support for the scientific community, which tends to lean on open ecosystems for the purposes of both sharing research and verifying results. Anthropic still describes MHS as being an application-only research preview. But they asserted that they intend to open-source MHS in the hope of it becoming an industry standard like MCP. Kemeny and Cool explained that they're first working with industry partners to test safety and security while the models are now operating on real-world equipment. It's also a fun note that since Cool has a PhD in cell biology, one of the leaders of this initiative is essentially named Dr. Cool. That kind of marketing is nearly as good as making it an open platform.
Can guardian agents make enterprise AI safer?
AI agents can act faster than humans can review them. So how do companies keep control without slowing everything down?
In this episode of The Deep View Conversations, Jason Hiner sits down with Blake Brannon, chief innovation officer and a co-founder of OneTrust, to explore why AI governance needs to evolve from static rules to decisions made in real time.
Brannon explains why an agent can inherit an employee's identity and access without inheriting their trust. He makes the case for independent guardian agents that evaluate what other agents are trying to do, apply a company's policies, and redirect or block actions when necessary.
One example captures the challenge: deleting CRM records could be routine cleanup or an attempt to inflate a salesperson's performance. The action alone doesn't tell you whether it should be allowed. Its purpose matters.
Topics covered:
• How OneTrust evolved from data privacy to AI governance
• Why first-party data and customer trust go together
• Why human review can't keep pace with a growing population of agents
• How guardian agents and independent checks could help close the trust gap
• The difference between containing AI and aligning it with business policies
• Why governance should help companies move faster
• What the bring-your-own-device era teaches us about AI adoption
• How Blake uses visual storytelling and voice-to-text tools to work more effectively
If you're deploying AI agents and trying to move beyond experiments without giving up control, this conversation offers a practical way to think about the systems that need to surround them.
📺 Watch on YouTube
🎧 Listen in your favorite podcast player
Subscribe to Deep View Conversations for interviews with the leaders shaping the future of AI, business, and technology: tdv.transitor.fm
How AI changes cybersecurity's balance of power
AI is accelerating cyberattacks. Could it also give defenders the upper hand?
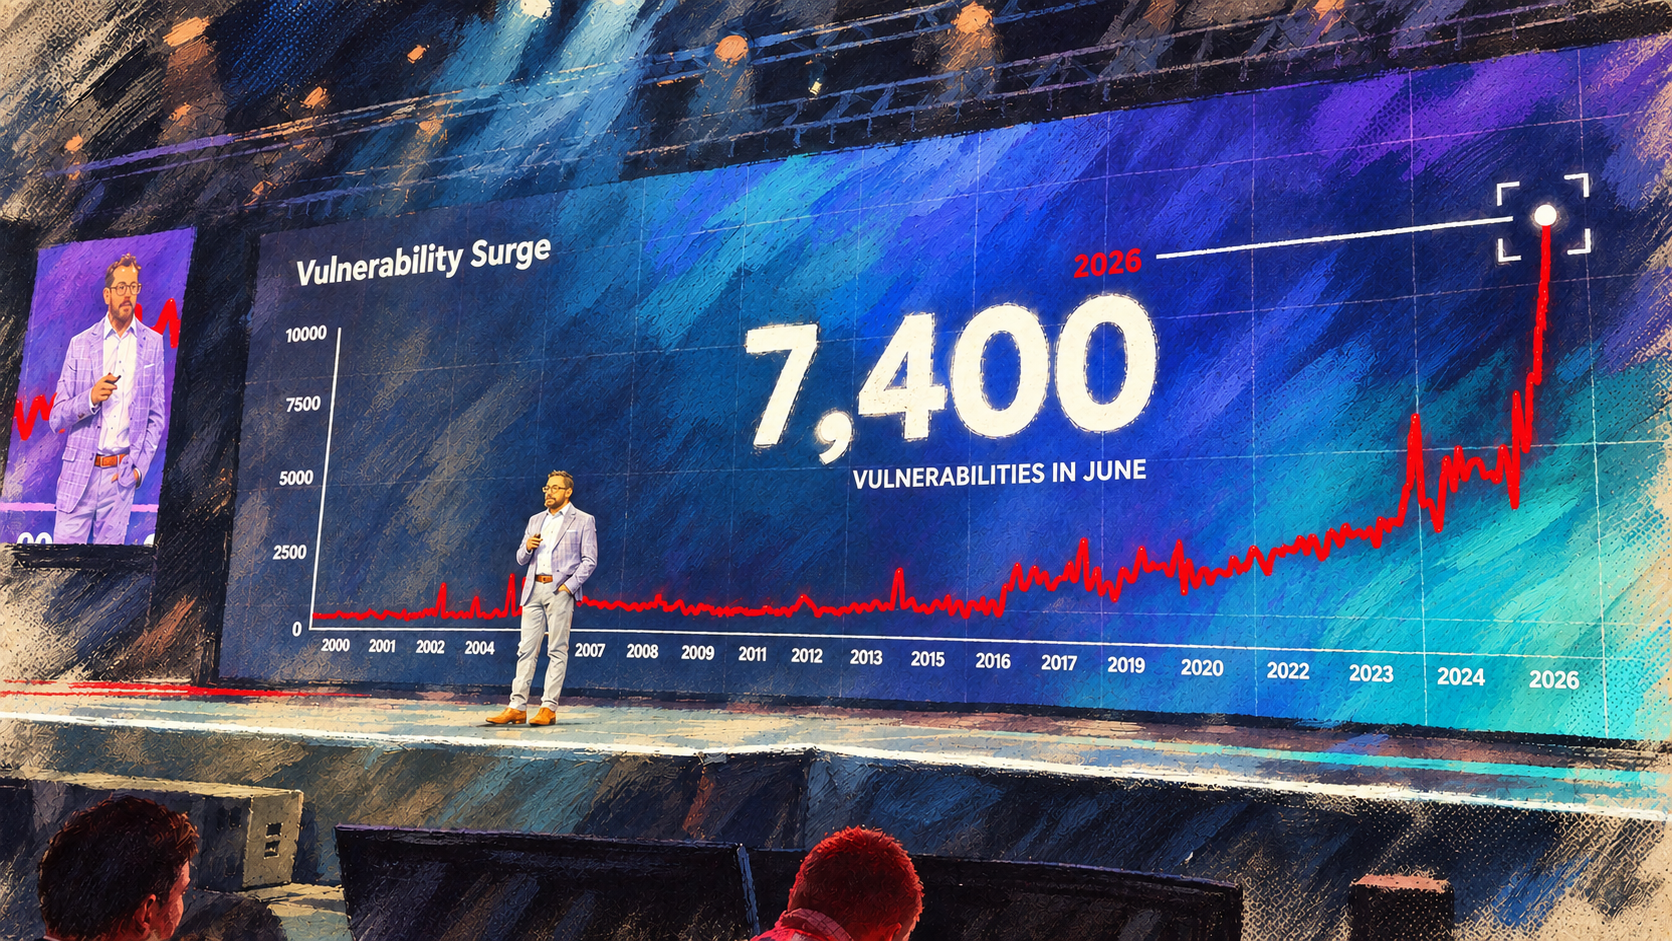
In this episode of The Deep View Conversations, we sat down with Adam Meyers, CrowdStrike's head of counter adversary operations, at Fal.Con 2026 to explore how AI is changing the balance of power between attackers and defenders.
Meyers explains why he believes security teams can now match the speed and scale of their adversaries, how CrowdStrike is training offensive and defensive AI models against each other, and why the harness that guides an AI model can matter just as much as the model itself. He shares how changing that harness helped CrowdStrike reduce false positives in its vulnerability research without changing the underlying model, and how cyberdefenders are uniting to assist one another.
The conversation also goes inside the live disruption of the Sality botnet, explores how nation-state attackers are using agents that learn from their mistakes in seconds, and examines why powerful AI systems need clear boundaries as they pursue their goals.
Topics covered:
• Why AI could change the defender's dilemma
• How CrowdStrike and its partners disrupted a botnet that had operated for more than two decades
• Training red team and blue team models based on Nvidia's Nemotron models and CrowdStrike's security data
• Why AI harnesses are critical to reducing hallucinations and false positives
• How AI attacks are compressing the time organizations have to patch vulnerabilities
• What the Hugging Face incident raises about goal-seeking agents and guardrails
• Why local, open-weight models matter to both attackers and defenders
If you're trying to understand what AI means for cybersecurity, how to put agents to work safely, or where specialized models can make a difference, this conversation offers a view from someone tracking the adversaries firsthand.
📺 Watch on YouTube
🎧 Listen in your favorite podcast player
Subscribe to Deep View Conversations for interviews with the leaders shaping the future of AI, business, and technology: tdv.transitor.fm
OpenAI rolls out deluge of new tools for AI builders
Heavy AI users rejoice. OpenAI has rolled out new options aimed at accelerating the stuff you're already doing and making it safer.
On Tuesday, at the company's fourth annual DevDay event in San Francisco, OpenAI showed off its new "Dots" strategy with AI agents that are always-on and run in their own separate cloud computer. Sound familiar? Yeah, it's not unlike Meta's new Muse agent that went viral this month, but OpenAI's agent is more focused on power users. See Sabrina Ortiz's full breakdown on Dots.
While Dots may have stole the headlines, OpenAI also unveiled other new features that dedicated ChatGPT and Codex users should note:
- GPT-6.1 Sol: OpenAI's latest model provides "near Astra intelligence" at a fifth of the price. The model sports improved performance in agentic coding, computer use and professional work, and runs $2 per million input tokens, 10 cents per million cached tokens, and $10 per million output tokens.
- ChatGPT Space: This is a collaborative workspace where you, your teammates and AI can work together. Spaces also allows users to keep everything they share with and create in ChatGPT in one place. It will also let you collaborate in a shared workspace similar to the way you might in a shared Google Doc.
- New $500/month plan and Ultrafast: OpenAI is creating a high-end tier that offers access to Ultrafast, which delivers up to eight times the speed in Codex using GPT-6 Astra and six times the speed in the API. However, For those on the $200 per month Pro plan, included usage of ChatGPT Work and Codex decreases from 20 times to 10 times that of the Plus allowance, and GPT-6 Pro messages in ChatGPT will be cut from 200 to 100 per week.
- Codex in the cloud: Codex can now start, review, and continue work from the desktop app, the mobile app, or the web. And since it's not limited to working on just the local files on your machine, you can move between devices much more easily.
- Plugin extensions: Developers can now build applications and plugins that are native to ChatGPT and Codex, and can reach more users with improved submission and discovery. And now those plugins will appear in the sidebar on the left side of your ChatGPT window, with services like Adobe and Figma being some of the first ones there at launch.
- Private Intelligence: OpenAI has enabled zero data retention and private safety processing policies for offline, automated safety reviews. Additionally, Private Inference will be available in preview, bringing strict control to confidential computing.
- OpenAI Marketplace: Eligible US-based enterprise customers can apply their existing OpenAI token spend towards approved third-party software. This marketplace is launching in beta with 32 partners, including Adobe, Figma, Sierra, and Harvey.
Our Deeper View
While it would be easy to look at OpenAI's DevDay as its answer to Meta's newfound momentum in the AI space, the reality is actually quite different. Meta's Muse agent is primarily focused on the consumer space and bringing agents to the masses with its focus on cute interactive avatars and wide publicity across Instagram and Facebook. OpenAI has lessened its focus on consumer AI in 2026 and leaned into enterprises, developers, and power users, and DevDay only doubled down on that strategy. Meta's agent is open to all and has generous token allotments based on Meta's strategy of eventually taking a percentage when you use Muse to sell stuff and make money. OpenAI is only offering its new agent to its highest-tier Pro and Business Premium customers. So OpenAI's focus is on its most-invested AI builders and organizations. And that strategy is supported by all of the other features it released around Dots on Tuesday, from Private Intelligence to GPT-6.1 Sol to its new Ultrafast feature. All of these things are aimed much more at competing with Anthropic for power users than competing with Meta for consumers.
Security's new dilemma: Agents reason differently
AI is accelerating familiar cybersecurity threats, but according to CrowdStrike's chief product officer AJ Shipley, speed and scale are only part of the story. AI agents can also assemble known tactics, techniques and procedures into unfamiliar attack chains, requiring existing security controls to adapt.
In a conversation with The Deep View at CrowdStrike's Fal.con event, Shipley discussed why organizations will need AI to defend against AI-enabled adversaries, how automation could change entry-level cybersecurity jobs, and why enterprises shouldn’t consider themselves outmatched. This interview has been edited for brevity and clarity.
Jason Hiner: How is AI changing cybersecurity?
AJ Shipley: I think, from my perspective, there's really two things that are interesting to think about from the perspective of the defender. One is something that we've been dealing with for the last several decades. It's just a matter of pace or how quickly things happen, and then the other one is net new, which is really interesting.
I think obviously AI-enabled adversaries are really just allowing those same bad actors to enumerate vulnerabilities and ultimately exploit vulnerabilities in order to further their means. Whether it's cyber warfare in advance of kinetic warfare, or whether it's stealing intellectual property, it's just allowing them to do that so much faster, and with so much more scale, as well as being able to find previously undiscovered vulnerabilities to then be able to exploit.
But for better or worse, the approaches to how you defend against that are the same approaches we've been using for the last 20 or 30 years. It's just a matter of pace on the defensive side. And so you have to use AI tooling in order to just be able to respond to the AI adversaries or the AI-enabled adversaries.
The other piece, though, which I think is really, really interesting, is the way these agents reason is fundamentally different than how people reason. And the last 10 or 20 or 30 years of security products have been built on this foundation of this intuitive understanding of how humans reason, either threat actors or adversaries or defenders, and how they're going to reason to try to respond to them.
What's different is that agents reason differently.... How these agents are putting together TTPs [tactics, techniques, and procedures] into attack chains that are fundamentally different than anything that we've ever seen before, and then how we have to be able to build defenses to those fundamentally different approaches to reasoning their way towards a problem, I think is something that we're very much focused on.
Jason Hiner: What makes AI agents so difficult for human defenders to handle?
AJ Shipley: These agents, I don't think, are inherently malicious or benign. I mean, I think you can probably build a malicious agent, but I think they are so task-oriented that they're going to try to find a way to accomplish their task, however they can.
Every TTP, every vector. I don't think that they're coming up with necessarily novel new techniques. Maybe they will in the future, but they're stringing TTPs together in a way, and then doing them at a pace and a scale that is impossible to respond to unless we are enabling the defenders with the same AI tooling.
I know that there's a zeitgeist out there around, "Hey, is AI and are agents going to replace security professionals?" I tend to be in the camp where I don't think that they will. And the reason for that is because there's two ways to increase productivity. You can do the same amount of work with fewer resources, or you can do more work with the same number of resources. Both of those are productivity gains.
I think in an AI-centric cyber world with an AI-enabled adversary, just the sheer scale means that we have to figure out a way to increase productivity. And one of the ways you can increase productivity is to do more work with the same number of resources. So those same number of resources are people. Which means, how are you going to enable those same number of people to do more work? With the AI tool.
That's what we're very much focused on: How do we use the agents or the tooling in order to make the defenders as productive as possible, not to replace the defenders? Because, again, I just think the data volumes are exploding, the way to chain together tactics and techniques in new, novel ways is exploding, and so you still need all of that expertise that people have. But we have to find a way to increase their productivity 10x or 100x.
Jason Hiner: How will AI change the work of cybersecurity analysts?
AJ Shipley: I definitely think that there are workflows, for lack of a better term, that AI will be able to fully automate away.
In the SOC [security operations center], we might say, "Hey, tier-one triage of just a whole bunch of alerts coming in." That's probably something that an agent's really good at. And then maybe some level of tier-one or tier-two investigation to figure out what's a true positive versus a false positive. That's probably something that an agent's really good at: doing that first gathering of evidence and synthesizing the evidence and coming up with a hypothesis, and then maybe testing some alternate hypotheses.
And I think that's where you still want a person in the role, stepping into that. And then the tier three, the incident response-type stuff: How am I going to take action now that I've confirmed that this is an incident?
I think this idea of what is an entry-level job probably moves up the stack from a tier one, tier two, tier three. Historically, entry-level was: You're going to be a tier-one analyst. You're going to start triaging a bunch of alerts. After a couple of years, we're going to let you start doing some investigation. And then when you get really good at it, we're going to let you do some incident response.
I think now we're going to start training humans and enabling them with tooling so that they don't have to do the tier-one menial-type work that they couldn't even keep up with anyways. Before, there was just this explosion of alerts, but now the whole idea of entry-level is just going to move up the stack, like a tier two or tier three.
That doesn't mean that this idea of entry-level jobs goes away. It means that what is the definition of entry level? It now becomes a higher-value skill set.
Jason Hiner: Will AI help organizations eliminate longstanding security weaknesses?
AJ Shipley: If you think about the cyber environment as a battle space, or a battlefield, there have always been advances in technology. Bronze Age, Iron Age, bow and arrow, gunpowder, naval warfare, atomic bombs. There have always been these advances in technology around quote-unquote warfare, where it felt like maybe at the time that the person who came up with the technology, or the side that came up with the technology, was like, "They're going to win". And then somebody else comes up with a way to defend against it. And then somebody else comes up with a clever way again to exploit it.
I tend to think that the AI tooling will expose where there's a lot of weaknesses where we didn't understand before. It will help us close a lot of those weaknesses. And if history is any guide, there will be something else that comes down the pipe in the future that exposes a whole bunch of new weaknesses that we're probably not even aware of.
I think that we will be a lot more informed on where there are vulnerabilities and where there are weaknesses, and then we will use the tooling to address those vulnerabilities and weaknesses. And in my experience, if history is any guide, there will be something else right around the corner in the future that we're then going to have to figure out: How do we respond and react to that as well?
I don't know what that thing is, but I tend to be an optimist. And just in general, I tend to think that when we figure that out, or when we encounter that thing, we'll figure out a way to defend against that as well.
Jason Hiner: What does the best-case outcome look like three to five years from now?
AJ Shipley: Five years is an eternity. If all goes well, I think we have built a fully redundant and resilient system, leveraging the tooling across all facets of the attack surface—endpoint, cloud, SaaS, network—to protect all of the assets that an organization cares about: their identities, human and non-human; the devices that those identities use to do their job; the applications that they use to do their job; the data that gets created.
Again, if all goes well, we've used really sophisticated and well-trained red models to identify vulnerabilities across all facets of that attack surface, and then we've used blue models to be able to remediate those vulnerabilities to the point where they're no longer exploitable. And then we can truly be able to take a vacation. That's the bull case, I think.
Jason Hiner: How can defenders account for the non-deterministic nature of AI models?
AJ Shipley: I think this idea of an ensemble of models, and having different models be able to vote on each other and weigh in, I think is ultimately what will address the non-deterministic nature, as well as harnesses.
I think there are mechanisms to be able to control the inputs such that you get a deterministic set of outputs. It's when little things change. For example, your input data set might be in a different schema. It might have a different timestamp. It might be asking the question slightly differently.
So I think a combination of harnesses, a combination of ensemble models, a combination of basically being able to get to weighted outcomes. And this is not all that much different, even from when I remember we were doing cloud-based sandboxing, malware analysis. You'd have a lot of different detection engines up there, and one detection engine might say that's malicious. One might say, "Not really sure." One might say benign.
And so how do the different detection engines, or the models at the time, the ML models, static or dynamic analysis, contribute to be able to make a determination of, "Hey, we think 80 or 90 percent of the way there that this is truly malicious."
Jason Hiner: What would you say to enterprises that fear they’re outmatched?
AJ Shipley: I would say they're not. They're not, at least in my opinion, they're not outmatched. Anytime there's been an inflection point in technology, technology has traditionally come along to significantly improve the productivity of civilization, and we've all benefited from it. AI is no different there. That technology obviously can be used for good, or it can be used for evil.
I would say embrace the technology, because it can be a productivity enhancer, and then make sure that you're partnering with somebody who's thinking about how to make sure that technology has the appropriate guardrails, that you have the appropriate visibility, that you can be able to detect when that technology is being used maliciously or inadvertently, and then you have all of the mechanisms and tools that you need to be able to respond to make sure that it doesn't happen again.
Some of what's old is new again. This is just an inflection point from a technology perspective. It's obviously driving a different pace that we have to be able to keep abreast of. But this technology doesn't use itself. It's not like there's an agent that just popped up out of the blue without somebody spinning up an agent and decided to go start acting rogue. There's people who are using this technology.
So partner with somebody who understands the adversary, who's always been focused on the adversary, is focused on understanding their tactics, their techniques and their procedures to partner with, so that you can then be an enabler of that technology in your organization in order to increase productivity.
How Meta suddenly re-emerged as a force in AI
As Meta emerges from rebooting its AI strategy, it's become clear that it's playing a different game than the other AI labs. It looks like it could be working.
At Meta Connect 2026 this week at the Meta headquarters in Menlo Park, California, we learned a lot more about the strategy Meta is deploying to earn a role in the AI ecosystem. Over the past few weeks, Meta's personal AI agent, Muse, has gone viral and become the No. 1 most downloaded app on Apple's App Store.
At Meta Connect, Muse was part of virtually every product line and every marketing pitch. Meta made it very clear that Muse is the centerpiece of its AI strategy, using both its AI models and its devices to serve the Muse strategy.
New developments include:
- Voice Mode: You'll soon be able to have natural voice interactions with Muse similar to ChatGPT Voice Mode and Siri AI, where you can interrupt it up and talk more conversationally. You'll be able to design and customize the voice based on talking speed, style, and accent.
- Realtime Avatar: Meta already gave its AI agent a more friendly consumer vibe by launching avatars that you can name and customize. It announced the next stage of that at Connect with the upcoming rollout of interactive avatars, which CEO Mark Zuckerberg demonstrated on-stage near the beginning of the keynote.
- Partner connectors: Meta announced a long list of partners that will be launching connectors for Muse, including GitHub, Box, Granola, Notion, PayPal, Instacart, Walmart, Best Buy, Gap, Dick's Sporting Goods, Wayfair, Michael Kors, and more.
- Computer use on Mac app: Meta has already launched a Mac desktop app (no Windows or Linux yet) and next it will be launching Computer Use, which will let you access other apps and sites that don't have connectors, among other things.
- Its own email address: Muse will soon get a dedicated email address that you can use for communicating with it, along with allowing it to do specific work on your behalf without using your email.
- Hands-free on AI glasses: Meta says you'll "soon" be able to call on your personal Muse agent by simply saying its name from Meta AI glasses and then asking it questions or assigning it tasks. If you use it from Meta AI glasses with cameras then you'll also be able to give it access to the cameras and ask it questions about things you're seeing.
- Charm pendant: The biggest surprise at the end of the Meta Connect keynote was Zuckerberg announcing a square AI pendant on keychain so that you will be able to access your Muse agent anywhere. Think of it as the AI hardware gadget for those who don't want to wear glasses. It will have a 2-inch OLED screen to see the Realtime Avatar of your muse, along with 5G for connectivity, two cameras, a fingerprint sensor, and mics and speakers. It's about the size of an AirPods case.
In the keynote, Meta's chief AI office, Alexandr Wang, also shared news of the company's next big leap forward in intelligence. He said, "Soon, we're dropping the most capable model we've ever trained. It's going to help our entire model family get smarter and more useful for everyone, including the models that power Muse."
Our Deeper View
Downloads of the Muse app are currently outpacing the meteoric launch of the ChatGPT iOS app in spring of 2023, but there's one big caveat. Meta runs one of the world's most powerful advertising platforms with Facebook and Instagram and it has been using it to drive massive numbers of downloads. It's smart and tells us a lot of consumers are interested in AI agents, but it doesn't tell us how many of them are actually setting up their own AI agent and starting to use it. OpenAI has shifted away from consumer apps in 2026 to focus on coding and enterprise like rival Anthropic, as both look to drive revenue and business model growth ahead of massive IPOs. Meanwhile, Meta has a treasure chest of revenue from its advertising business that it can use to play the long game on consumer AI. It also has the consumer relationships and the in-house expertise for running consumer brands, and it shows in how friendly it has made Muse—by far, the easiest agent to get up and running. The big question, of course, will be trust. Meta will need to convince consumers to trust it with some of their most important and most private data in order for its agent to have the context it needs to be effective. While it's good to see Meta taking steps like the Muse Secure VM to ensure privacy, it's going to need to demonstrate consistently that it's making privacy and security a top priority. That's because trust comes in on foot and goes out on horseback, as the saying goes. And given Meta's challenging track record, the company will need to change the narrative and entice some people to come back in.
Disclaimer: Jason Hiner's travel to Meta Connect 2026 was paid for by Meta. The Deep View's coverage is editorially independent from the companies we cover.
AI safety needs more than good intentions
Can AI move fast and still be safe? As the debate over AI safety and innovation grows more polarized, we explore the practical work of making powerful systems accountable.
In this episode of The Deep View Conversations, we sit down with Navina Singh, CEO of Credo AI, to talk about what AI governance means for frontier labs, enterprises, and policymakers. They explore why governance is broader than regulation, how organizations can test and verify their AI systems, and what happens when capabilities advance faster than oversight.
Topics covered:
• Why Navrina sees AI safety and innovation as goals that can advance together
• What the Hugging Face agent incident raises about frontier AI oversight
• The “spectrum of trust,” from internal testing to independent audits and regulation
• The risk of regulatory capture and the role of open models
• How businesses weigh AI capability, cost, and control while managing "governance debt"
• How Credo AI uses forward-deployed governance experts to help companies put oversight into practice
• Why expertise, taste, and judgment remain valuable as AI takes on more work
If you’re building, buying, or governing AI, this conversation offers a practical way to think about trust without losing sight of the technology’s promise.
📺 Watch on YouTube
🎧 Listen in your favorite podcast player
Subscribe to Deep View Conversations for interviews with the leaders shaping the future of AI, business, and technology: tdv.transitor.fm
or get it straight to your inbox, for free!
Get our free, daily newsletter that makes you smarter about AI. Read by 750,000+ from Google, Meta, Microsoft, a16z and more.